Improve Product Security and Software Quality with Static Code Analysis
In this webinar, we explore how static code analysis can help improve software quality, strengthen product security, and support Cyber Resilience Act (CRA) compliance. We also discuss practical approaches to improving your codebase, meeting CRA documentation requirements, and addressing common software development challenges.
The webinar covers the following topics:
- Understand how the CRA impacts your business
- Learn what technology is available to help you
- Supercharge your software development capability
- Use secure-by-design principles to differentiate in your field and turn a cost into a benefit
Authors
Mark Hermeling
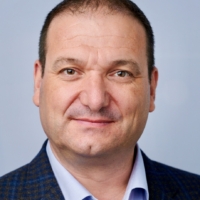
Mark has over 25 years’ experience in software development tools for high-integrity, secure, embedded and real-time systems across automotive, aerospace, defence and industrial domains. As Head of Technical Marketing at AdaCore, he links technical capabilities to business value and is a regular author and speaker on on topics ranging from the software development lifecycle, DevSecOps to formal methods and software verification.
Martin Andersson
At Nohau, Martin is supporting Nohau's customers with all sorts of problems, from installation/license issues, setting up hardware/communication (CAN,RS232, etc.) to learning how to use the tool and being a teacher of embedded C development.
He has extensive experience in development with C for embedded systems where both software architecture, "board bring-up", hmi and various communication interfaces (CAN, Ethernet, rs232, ISOBUS etc.) are among his usual challenges.